

The best defense anticipates the offense and moves faster than it does. Finding a vulnerability and fixing it used to happen on roughly the same timeline. That's no longer the case.
Discovery now moves at machine speed, yet remediation still largely moves at human speed. Analysts triage thousands of exposure findings a day, and many sit open for weeks. No one has the capacity to act on them all.
In my last post, I made the case that reacting after the fact is a losing strategy, and that preemptive cybersecurity should anchor the enterprise. The best incident is still the one that never happened. But foresight has a limit: it tells you what's coming, not who has time to act on it.
Agentic exposure management is the missing piece.
What is agentic exposure management?
Agentic exposure management is the practice of using autonomous agents to run continuous end-to-end threat exposure management. The agent monitors the enterprise, weighs each exposure against business impact, exploitability, and control efficacy, and acts when policy permits.
That means the systems that find exposures can now reason about them, decide on the right response, and close them within policy guardrails. Preemptive security alerts you to a threat. Agentic exposure management acts on it.
Why anticipation is no longer enough
Attackers are already automating the full kill chain, from scanning for weaknesses to writing the exploit to deploying it, without a human in the loop. Defenders can't say the same. Most exposure findings still wait for a person to read them, judge them, and decide what to do.
Agentic exposure management reconciles that mismatch, giving preemptive defense the reflexes and policy controls to act on what it sees, resulting in:
- Faster remediation: Routine exposures close in minutes rather than days.
- Analyst time reclaimed: Triage hours shift to the handful of exposures that genuinely threaten the business.
- A structural answer to the talent shortage: Agents scale where hiring alone cannot.
What to settle before you let agents act
Moving to agentic exposure management is one of the largest trust leaps enterprise security teams are taking. It touches governance, legal accountability, and culture just as much as technology. Here’s what to work out before you begin.
- Contain the blast radius. The speed that makes an agent valuable is the same speed that can make a mistake costly. Contain that risk with rigorous scoping, reliable rollback, and the discipline to withhold autonomy from anything the organization cannot afford to get wrong.
- Build in accountability. When an autonomous action goes wrong, someone needs to own it. Regulators, auditors, and boards will not accept "the agent decided." Every autonomous decision needs a clear chain of reasoning, a governance policy that authorized it, and a named human accountable for the outcome.
- Feed agents clean data. Agentic reasoning amplifies whatever data it receives. Fragmented telemetry and inconsistent identity data produce confident, wrong decisions. Data hygiene is what makes the rest possible.
- Close the governance gap. Many enterprises lack an agent registry or a policy layer that governs what agents may do. For every agent, answer four questions: What can it do? What data can it reach? Who authorized it? How do we prove it stayed in its lane?
- Defend the agents themselves. Prompt injection, poisoned telemetry, model drift, and agent identity spoofing are already being weaponized. We protected our detection AI. Now we need to protect our decision AI, with continuous red teaming as a standing discipline.
- Prepare people to work with agents. Analysts who have spent years as the last line of defense may resist an AI colleague making decisions. Others may trust it too readily and stop questioning its output. Both extremes slow adoption. Deliberate change management, including training on when to trust an agent and when to challenge it, builds a healthy human-agent partnership.
Set the ground rules before the first agent goes live. Define your risk appetite, name who owns agent governance, and list the actions agents may never take. Then agree on how you will measure success from day one: mean time to remediate, exposure dwell time, and autonomy ratio, the share of exposures closed without human intervention.
The remediation funnel: matching autonomy to risk
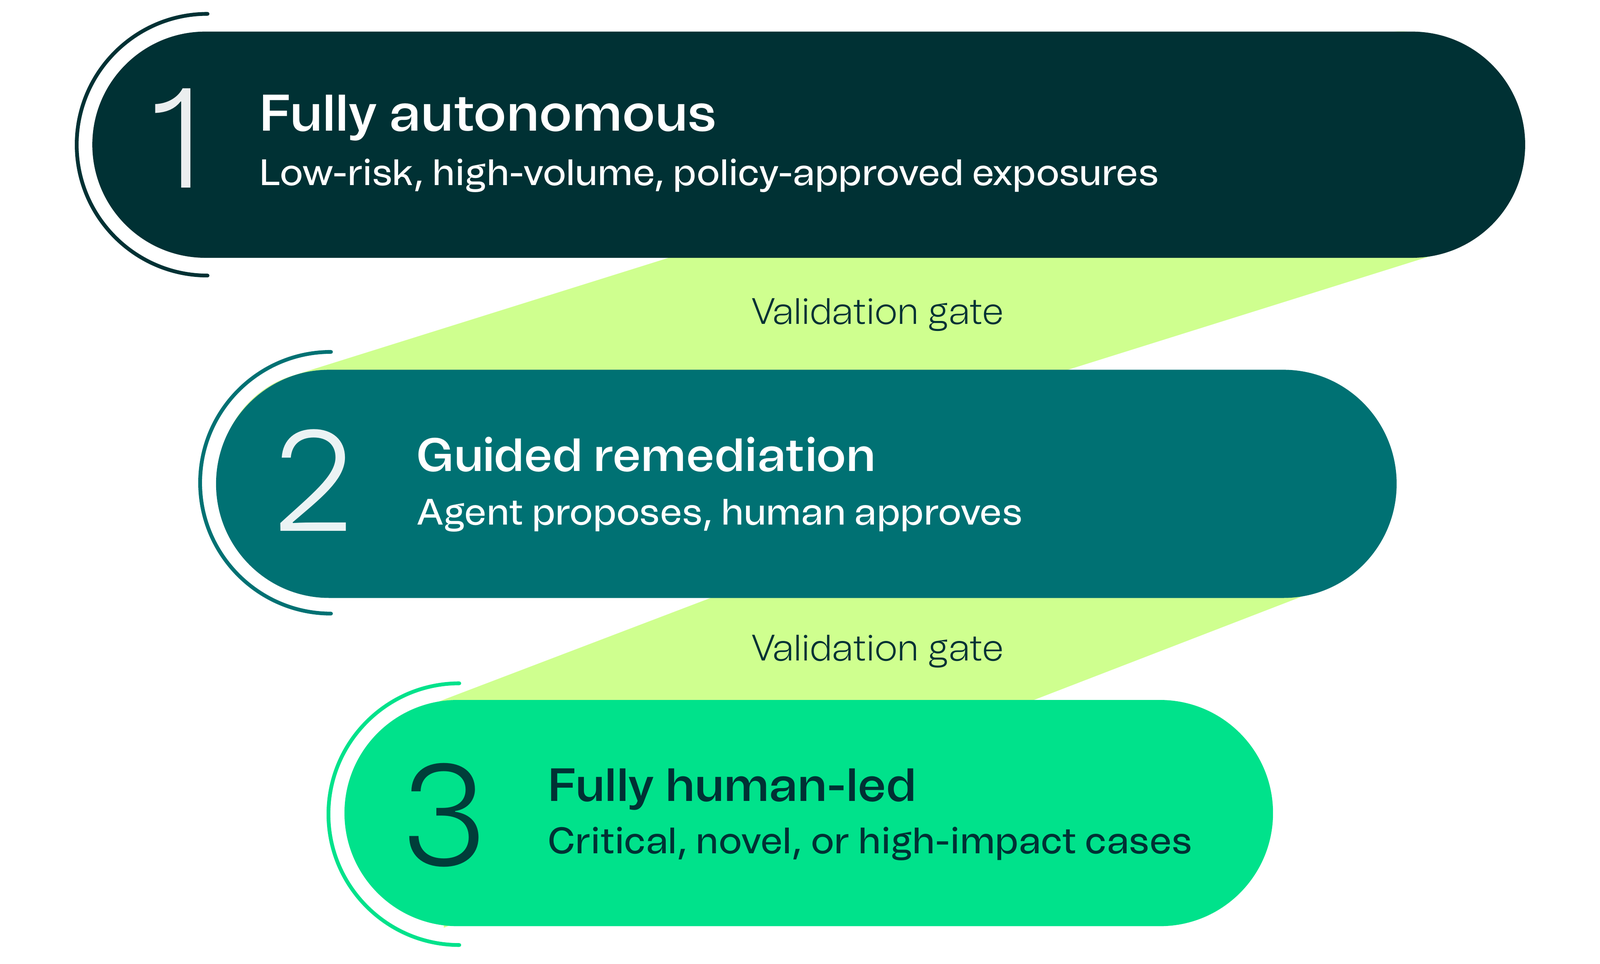
The considerations above are guardrails. The funnel is how you apply them, deciding upfront and by policy which class of exposure gets which class of response. (See Figure 1.)
Not every exposure deserves the same response. A remediation funnel sorts exposures into tiers, from fully autonomous to fully human-led, with a validation gate between each one. Low-risk, high-volume, policy-approved exposures move through untouched by human hands. Critical, novel, or high-impact cases wait for a person. The funnel also makes governance visible to stakeholders, showing what was closed autonomously, what required a human, and why.
Trust has to be earned in stages. Start with the smallest, safest slice of exposures, prove the agent, and expand its authority from there. Review its decisions weekly for the first six months, and treat every near miss as a lesson. Every agent that reaches production should meet three conditions:
- Controlled: Gates separate reasoning from execution, with every action validated in a digital twin and ready to roll back.
- Trusted: Only approved tools and models, working within tightly scoped policy boundaries.
- Governed: A registry entry, a full audit trail, and a named owner accountable for every decision.
What it looks like in practice
Agentic exposure management ceases to be an abstraction the moment it encounters real security issues.
- Autonomous patching handles known vulnerabilities on non-critical assets inside pre-approved change windows. The agent acts within policy guardrails, and the analyst audits after the fact.
- Automated validation and rollback verifies each configuration change in a digital twin before rollout, then restores the approved configuration if it drifts. The agent proposes the fix, and a human approves by exception.
- Guided response assembles a full evidence pack on a suspected supply-chain compromise in minutes, so a human can decide right away.
- Emergency orchestration supports the response team during active ransomware or zero-day exploitation. Under controlled, trusted, and governed conditions, agents take on repetitive work at machine speed so analysts can focus on the decisions.
Four different situations. One pattern: the agent handles what it's trusted to handle, and hands off the rest to a person, fast enough that the handoff itself is never the bottleneck.
Foresight and reflexes, working together
Preemptive cybersecurity gives defense foresight. Agentic exposure management gives it reflexes: the ability to act, learn, and improve at machine speed, under human command. Together, they let defense spot risk early and act on it before it becomes a breach.
Agents close exposures quickly and within policy, with a full audit trail documenting every decision. The best incident is still the one that never happened, and the best exposure is the one closed before anyone can exploit it. Every exposure an agent closes frees an analyst for the work only humans can do and helps defense keep pace with today's threats.
Ready to give preemptive defense its reflexes? Unisys offers agentic exposure management as part of our AI-first cybersecurity portfolio, backed by decades of managed services experience and a governed framework that matches every exposure to the right tier of autonomy. Controlled, trusted, and governed guardrails give your teams the confidence to let agents act where humans no longer need to.
Explore Continuous Threat Exposure Management and Unisys Security Managed Services to get started.